Service
DevSecOps
Deployments that stop being an event, with a rollback anyone on the team can run. Security runs inside the pipeline, where the change is.
The seam this closes
Between writing the change and it being safely live, usually a manual step held by one person.
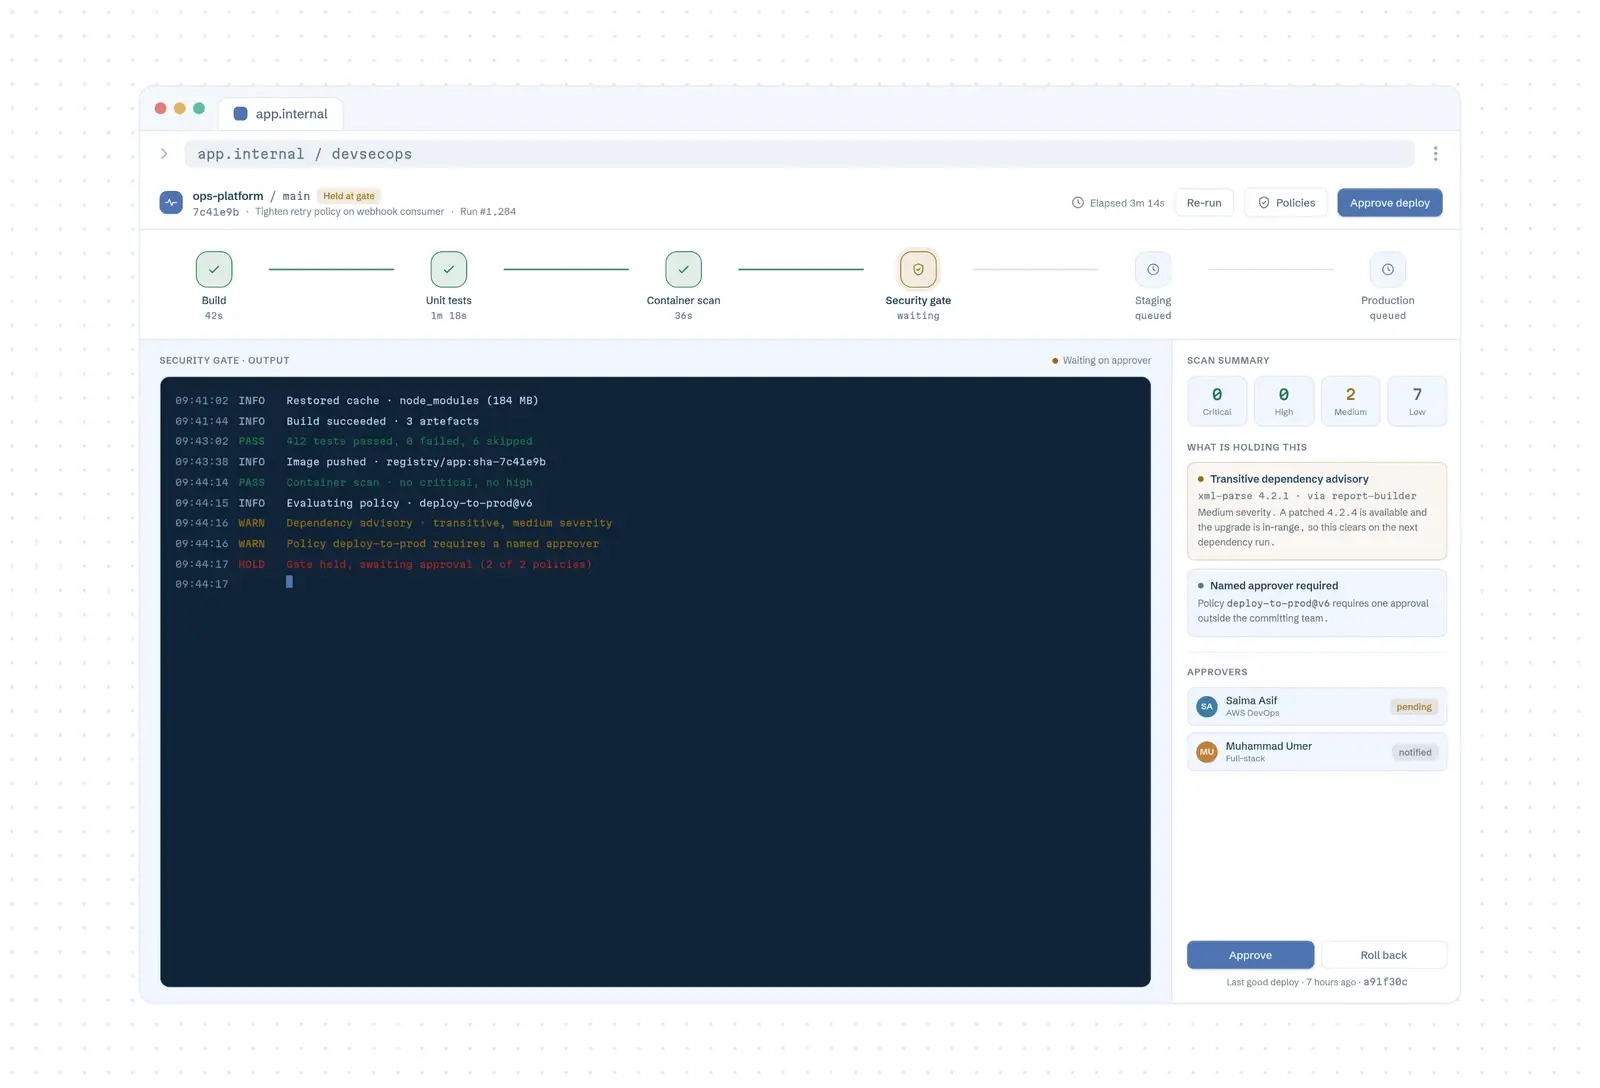
What gets built
- CI/CD pipelines with a rollback you have tested
- Infrastructure as code, so environments match each other
- Container orchestration sized to what you actually run
- Secrets, scanning and policy enforced in the pipeline
What this is not
Kubernetes is never the default answer. Plenty of businesses are correctly served by something much simpler, and we will tell you if yours is one.
Start with the seam that is costing you the most.
A first call is a scoping conversation. If there is no system worth building, we will say so.